+91-8115609560, ajai@sevenstepconsulting.com

SOC 2
Below is a conversion-focused landing page designed specifically for Seven Step Consulting. It is written to improve SEO, engage decision-makers, and increase inquiries. The content naturally targets keywords such as SOC 2 Compliance Services, SOC 2 Consultant India, SOC 2 Readiness Assessment, SOC 2 Type 1, and SOC 2 Type 2.
SOC 2 Compliance Services | Trusted SOC 2 Consultants in India
Build Trust. Win Enterprise Customers. Achieve SOC 2 Compliance with Confidence.
Enterprise customers expect more than promises—they expect proof that your organization protects their data.
SOC 2 compliance has become a critical requirement for SaaS companies, cloud providers, technology firms, fintech organizations, healthcare companies, AI startups, and managed service providers looking to grow globally.
At Seven Step Consulting, we help organizations achieve SOC 2 compliance through a practical, business-focused approach that reduces complexity, accelerates audit readiness, and strengthens cybersecurity governance.
With over 20 years of industry experience, our consultants have helped hundreds of organizations implement internationally recognized security and compliance frameworks, enabling them to build trust, reduce risk, and win more business.
VS
Why SOC 2 Matters
Today, enterprise customers routinely ask vendors questions such as:
How do you protect customer information?
Are your security controls independently verified?
Can you demonstrate compliance with recognized international standards?
How do you manage cyber risks?
Is your organization prepared for security incidents?
A SOC 2 report answers these questions with independent assurance that your organization has implemented effective controls to protect customer data and operate securely.
For many organizations, SOC 2 is no longer optional—it is a competitive advantage that helps shorten sales cycles, satisfy procurement requirements, and unlock new market opportunities.
What is SOC 2?
SOC 2 (Service Organization Control 2) is an internationally recognized assurance framework developed by the American Institute of Certified Public Accountants (AICPA).
It evaluates the effectiveness of your organization’s controls against five Trust Services Criteria:
- Security
- Availability
- Processing Integrity
- Confidentiality
- Privacy
Unlike a certification, SOC 2 is an independent attestation performed by a licensed CPA firm, providing customers with confidence that your controls are designed and operating effectively.
SOC 2 Type I vs SOC 2 Type II
SOC 2 Type I
- Evaluates whether your security controls are properly designed at a specific point in time.
- Best suited for organizations beginning their compliance journey.
SOC 2 Type II
- Evaluates whether your controls operate effectively over a defined period, typically three to twelve months.
- Most enterprise customers prefer or require a SOC 2 Type II report because it demonstrates sustained operational effectiveness.
Our consultants help you prepare successfully for both engagements.
Our End-to-End SOC 2 Consulting Services
SOC 2 Readiness Assessment
- Understand your current maturity through a detailed gap assessment against the Trust Services Criteria.
Deliverables include:
- Executive readiness report
- Compliance maturity assessment
- Risk analysis
- Gap identification
- Prioritized implementation roadmap
2. SOC 2 Gap Analysis
Our experts identify deficiencies in:
- Information Security
- Governance
- Risk Management
- Access Controls
- Vendor Management
- Incident Response
- Change Management
- Business Continuity
- Privacy
- Monitoring and Logging
3. Policy and Documentation Development
We develop or enhance documentation including:
- Information Security Policy
- Access Control Policy
- Risk Management Policy
- Incident Response Plan
- Vendor Security Policy
- Change Management Procedures
- Business Continuity Plan
- Disaster Recovery Plan
- Asset Management Policy
- Acceptable Use Policy
- Data Classification Policy
- Employee Security Handbook
4. Security Control Implementation
Our consultants work alongside your teams to implement practical controls covering:
- Identity and Access Management
- Multi-Factor Authentication
- Endpoint Security
- Vulnerability Management
- Risk Assessment
- Logging and Monitoring
- Secure Development Practices
- Vendor Risk Management
- Security Awareness Training
5. Audit Readiness Support
Before your external audit, we help you:
- Validate evidence
- Review policies
- Conduct mock assessments
- Close remaining gaps
- Prepare management responses
- Support auditor interactions
6. Continuous Compliance Support
SOC 2 is not a one-time exercise.
We provide ongoing services including:
- Quarterly Compliance Reviews
- Internal Audits
- Risk Assessments
- Control Monitoring
- Policy Updates
- Management Reviews
- Continuous Improvement
Why Organizations Choose Seven Step Consulting
Unlike firms that simply provide templates, we build practical compliance programs that strengthen your business.
- 20+ Years of Industry Experience
- Trusted advisors in cybersecurity, governance, risk management, and compliance.
- Practical Implementation
- Solutions designed for real business operations—not just passing an audit.
- International Expertise
Experience with:
- SOC 2
- ISO/IEC 27001
- ISO/IEC 27701
- ISO 22301
- HIPAA
- GDPR
- India’s Digital Personal Data Protection Act (DPDPA)
- ISO/IEC 42001 AI Management Systems
Experienced Consultants
Our consultants bring decades of leadership experience from global organizations and understand both technical and business requirements.
Integrated Compliance Saves Time and Cost
Many organizations need multiple compliance frameworks.
Instead of implementing separate programs, we build a unified governance framework that allows controls and evidence to be reused across:
- SOC 2
- ISO/IEC 27001
- ISO/IEC 27701
- DPDPA
- HIPAA
- ISO/IEC 42001
- NIST Cybersecurity Framework
This integrated approach reduces duplication, lowers implementation costs, and simplifies ongoing compliance.
Industries We Serve
We help organizations across industries including:
- SaaS
- Artificial Intelligence
- Cloud Computing
- Financial Services
- FinTech
- Healthcare
- HealthTech
- Information Technology
- Managed Service Providers
- Business Process Outsourcing
- E-commerce
- Manufacturing
- Logistics
- Education Technology
- Professional Services
Benefits of SOC 2 Compliance
- Organizations that achieve SOC 2 compliance often experience:
- Increased customer confidence
- Faster enterprise sales
- Stronger cybersecurity governance
- Improved operational resilience
- Better risk management
- Enhanced investor confidence
- Competitive market differentiation
- Reduced security incidents
- Improved regulatory readiness
Our Proven Seven Step Consulting Methodology
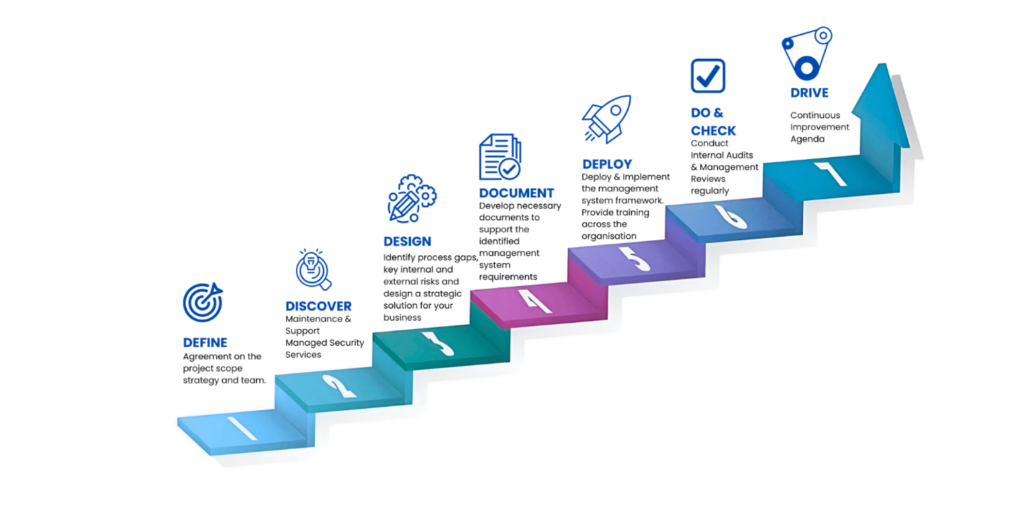
- Define : Agreement on the Project Scope, Strategy and Team
- Discover : Understand your business, risks, and objectives.
- Design : Identify process gaps, key internal and external risks and design a strategic solution for your business
- Document : Develop necessary documents to support the management system requirements and write and approve policies, controls, and governance processes.
- Deploy : Deploy and implement the management system framework and provide training across the organization Develop a practical implementation roadmap
- Do & Check : Conduct Internal audits and Management Reviews to evaluate existing controls and identify compliance gaps.
- Drive : Build a culture of continuous compliance and security excellence.
Common Questions
How long does SOC 2 implementation take?
Most organizations achieve audit readiness within 3–6 months, depending on their current security maturity and the scope of the engagement.
Do startups need SOC 2?
Yes. If you sell to enterprise customers or manage sensitive customer data, SOC 2 is often a prerequisite for doing business.
Can SOC 2 be integrated with ISO 27001?
Absolutely. Many controls overlap, allowing organizations to reduce effort and implementation costs through an integrated compliance program.
Can Seven Step Consulting help with the external audit?
Yes. While the final attestation is performed by an independent CPA firm, we support your organization throughout the readiness, implementation, evidence collection, and audit preparation phases.
Do you support the India DPDP Act?
Yes. ComplAi is purpose-built for the DPDP Act 2023, with consent management, data governance, and audit-ready tracking.
Ready to Scale Compliance Across Every Industry?
ComplAi adapts to your industry, business maturity, and regulatory requirements helping you achieve compliance faster, manage risk proactively, and strengthen governance at scale.